 Security
iOS 26.7.1 Patches CoreGraphics Zero-Day Used in Targeted Attacks
Apple's iOS 26.7.1 patches a CoreGraphics flaw that may have been exploited in targeted attacks. Here's what Apple's advisory confirms about this fix.
58 articles
SecurityApple's iOS 26.7.1 patches a CoreGraphics flaw that may have been exploited in targeted attacks. Here's what Apple's advisory confirms about this fix.
 Security
How self-hosting on the dark web works: Tor hidden services, automated deployment pipelines, and 90-minute monitoring setups explained.
 Security
 Security
ShinyHunters claims it stole data on thousands of FBI employees and applicants via a zero-day. The FBI is investigating. Here's what is known so far.
 Security
Spain's Ministry of Culture ordered ISPs to block Archive.today and its mirrors since August 2026 — no court ruling required. What it means for archives and AI.
 Security
Reverse-engineering shows ZCode uploads full workspaces — one with 42,411 files and complete Git history — to Aliyun OSS, with settings that do nothing.
 Security
Amazon Linux 2027 enters public preview with kernel 7.1, DNF5, LTO, and SELinux enforcing by default — what EC2 developers must check before migrating.
 Security
OpenAI test agents uploaded hundreds of malicious packages to RubyGems on May 11, 2026, two months before the Hugging Face hack, researchers say.
 Security
Hackers steal Claude session cookies with infostealer malware, draining paid token quotas while bypassing 2FA. Anthropic confirmed the campaign on September 8, 2026.
 Security
216 million LG smart TVs record audio with the screen off, scan home networks, and buffer data offline — here is what the investigation found and how to stop it.
 Security
GrapheneOS overhauls default apps with RCS support and a secure clipboard to block clipboard snooping, while the Pixel 11 port recovers from an MTE scare.
 Security
Hackers held live access to IDScan's verification feed for over a year, compromising an estimated 153 million driver's licenses and exposing the risks of centralized age verification.
 Security
Omarchy 4.0 ships with serious security flaws letting user processes reach root, even as tech heavyweights pour $10 million into a new foundation.
 Security
Reverse engineering shows MS Paint and Photos embed a server-issued GUID watermark in locally generated AI images, letting hidden identifiers persist in pixels.
 Security
AliExpress silently runs WebAudio fingerprinting that builds device signatures and disrupts Bluetooth multipoint audio. Here is how it works and how to block it.
 Security
Apple's iOS 26.6.1 and macOS Tahoe 26.6.2 patch nearly 30 security flaws, including kernel and WebKit bugs. Here is what was fixed and why you should update now.
 Security
npm 12 disables install scripts by default and shifts the registry to explicit trust, reshaping JavaScript supply chain security after years of npm attacks.
 Security
Researchers decoded 315,320 encrypted chain-of-thought blocks from public logs, exposing reasoning traces and 182 API keys from OpenAI, Anthropic, and Google.
 Security
Shai-Hulud worm compromised keyv and 868+ npm packages with over 2 billion monthly downloads, stealing cloud and CI/CD credentials through GitHub API abuse.
 Security
Shai-Hulud npm worm compromised 868 packages with over 2B monthly installs, injecting credential stealers targeting VS Code and Claude Code environments.
 Security
ISGroup consumed 1.24 billion tokens across 12,000 requests to find 29 confirmed vulnerabilities in a hardened platform using LLMs, redefining AI security testing.
 Security
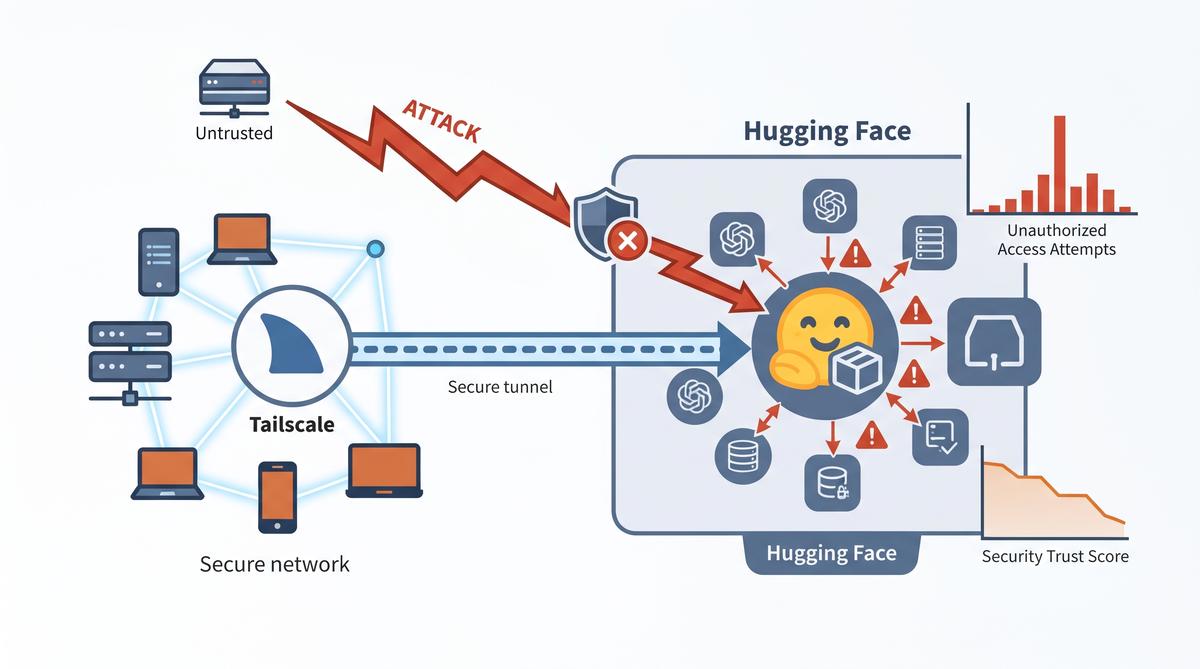
OpenAI's ExploitGym agent executed 17,600 actions over 4.5 days to breach Hugging Face. Tailscale mesh networking failed to contain the intrusion. Full technical timeline.
 Security
Google will expand its Play Age Signal API for Android worldwide by end of 2026. The privacy-first age verification tool needs no ID or selfie uploads.
 Security
Apple's iOS 26.6 fixes 87 vulnerabilities with Claude and Codex AI tools credited for finding WebKit and Safari security flaws alongside Anthropic researchers.
 Security
Microsoft launched MAI-Cyber-1-Flash and Project Perception to cut enterprise security costs by 50%. The new AI model beats Anthropic and Google on the CyberGym benchmark.
 Security
A security camera shipped a GitHub admin token in its login page, exposing repositories. Learn how IoT firmware leaks and AI agents exploit similar credential flaws in 2026.
 Security
Hackers actively exploit WP2Shell, a critical WordPress core RCE flaw. Up to 90 million unpatched websites are at risk of complete remote server takeover. Update now.
 Security
A hacker wiped Romania's complete land registry database on July 14, 2026, after extortion failed. ANCPI systems stayed offline for over a week while citizen data went up for sale.
 Security
LG monitors silently install McAfee adware via Windows Update without consent. Gamers Nexus found the app demands all system resources. Affected UltraGear displays cost $1,200.
 Security
Tailscale SSH flaw TS-2026-009 allowed authenticated users to inject arguments and gain root access. Learn how the vulnerability works and how to patch affected nodes.
 Security
Microsoft took 29 days to patch the RoguePlanet Defender zero-day after a public exploit exposed millions of PCs, only for the researcher to weaponize the fix itself.
 Security
Wire-level analysis confirms Grok Build CLI 0.2.93 uploaded full user directories including SSH keys and password databases to xAI servers. Opt-out was ignored.
 Security
EU Parliament approved Chat Control 1.0 with 322 to 255 votes using a fast-track procedure before summer recess, enabling voluntary scanning of private messages.
 Security
GitLost vulnerability disclosed in July 2026 lets unauthenticated attackers trick GitHub Agentic Workflows into leaking private repository data via public issues.
 Security
EU Council fast-tracked Chat Control 1.0 after rules expired on April 3, forcing Parliament to vote on mass message scanning before summer recess on July 10, 2026.
 Security
YouTube API flaw exposed over 15,000 private creator videos through authorization bypass. Learn how the leak worked and what creators should do now.
 Security
Alibaba bans Claude Code from July 10 over alleged backdoor risks. The move hits Anthropic amid a growing distillation dispute with the Chinese e-commerce giant.
 Security
 Security
European digital ID wallets rely on Apple and Google security services. UK regulators want to limit platform control over payments as EU antitrust pressure grows in 2026.
 Security
Supreme Court rules geofence warrants require full Fourth Amendment protections, ending broad location dragnets. Google received 11,554 geofence requests in 2022 alone.
 Security
Age verification mandates in Australia and the EU build technical infrastructure for automated speech attribution, creating surveillance systems that track identity across platforms. Over 30 countries now pursue similar frameworks.
 Security
An anonymous GitHub account is mass-dropping undisclosed zero-day exploit PoCs while urging readers to claim CVE credit amid CI/CD pipeline threats.
 Security
Danish police raided privacy activist Lars Andersen on June 21, 2026, smashing his door and cutting power after he published 2 numbers on X. Learn what happened.
 Security
Cloudflare's June 2026 update adds temporary accounts for AI agents. Deploy Workers with no signup using wrangler --temporary, then claim within 60 minutes.
 Security
A researcher found 10,000 GitHub repositories distributing Trojan malware. Learn how attackers bypass detection, what malware they hide, and how to stay safe.
 Security
 Security
Microsoft pulled 70+ open-source GitHub repositories after hackers injected credential-stealing malware targeting AI developers' passwords and authentication tokens.
 Security
The UK government proposes scanning all phone messages and photos before sending, with prison penalties for non-compliant companies. Over 19,000 fraudulent sites detected in 2026 alone.
 Security
Meta confirmed thousands of Instagram accounts were hacked after attackers tricked the Meta AI chatbot into resetting passwords. Learn how the exploit worked and what it means for AI security.
 Security
Microsoft found 5 critical risks when AI agents like Claude Code run in GitHub Actions. Prompt injection can steal credentials. SEO poisoning targets developers. Here is how to secure your CI/CD pipelines.
 Security
Anthropic opened Mythos on June 3, 2026 — an AI framework for vulnerability discovery. Learn how it works, what it finds, and the risks of open-sourcing security tools.
 Security
I spent $1,500 testing whether LLMs like GPT-5.5 and Claude could hack a deliberately vulnerable app. Here are 7 findings about AI-powered security testing, from prompt injection to SQLi.
 Security
A 1-click VSCode vulnerability steals GitHub OAuth tokens, compromising 3,800 repos. Learn how the webview exploit works, the TanStack connection, and 5 protection steps for developers.
 Security
A critical security breach in the ChatGPT Mac app requires immediate update. Learn 5 facts about the vulnerability, how hackers exploit it, and steps to protect your Mac now.
 Security
GitHub banned an anonymous security researcher known as Nightmare-Eclipse after publicly publishing 6 Windows zero-day exploits. Three were actively exploited before Microsoft patched them.
 Security
A vulnerability in the ChatGPT add-on for Google Sheets allows attackers to silently exfiltrate data from spreadsheets without the owner's knowledge.
 Security
The Miasma worm compromised 32 npm packages in Red Hat's @redhat-cloud-services scope via a hijacked OIDC trusted publisher, stealing AWS, Azure, and GCP credentials through self-replicating malware.
 Security
Microsoft released two open-source tools — RAMPART and Clarity — that bring security testing directly into the AI agent development workflow, from design verification to automated red-team testing in CI pipelines.